The Greatest Fear of Every Noob Cybersecurity Analyst
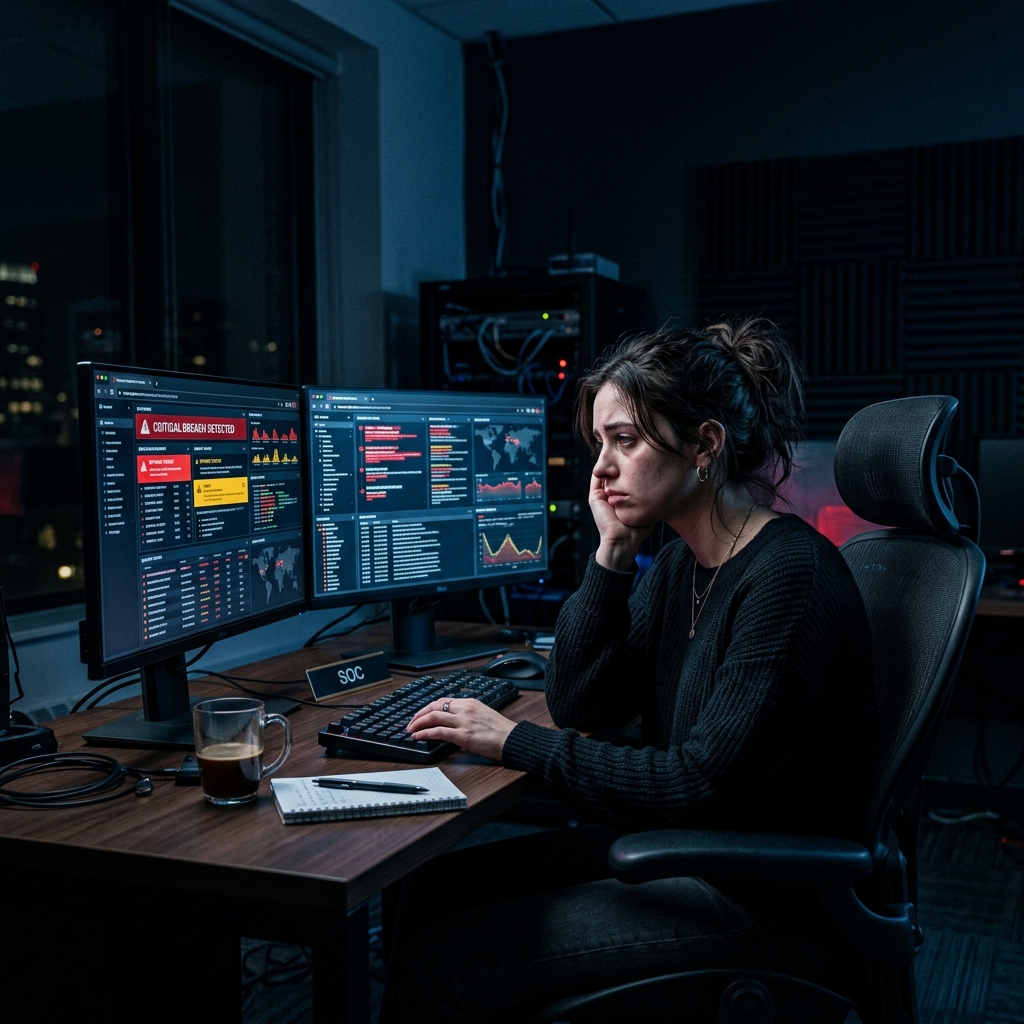
You know that moment when you land your first role and you're staring at a dashboard full of alerts — red, yellow, critical — and your brain just goes blank? Yeah. Let's talk about that. Because the fear isn't that you'll miss something. The fear is that you'll miss something and everyone will know.
You know that moment when you land your first role and you're staring at a dashboard full of alerts — red, yellow, critical — and your brain just goes blank?
Yeah. Let's talk about that.
Because the fear isn't that you'll miss something. The fear is that you'll miss something and everyone will know.
Every noob analyst has this silent terror running in the background like a rogue process. You've studied the frameworks. You've read the blogs. You've passed (or you're about to pass) the certs. But nothing prepares you for the moment a real alert fires and someone senior turns to you and says, "What do you think?"
And suddenly, everything you thought you knew evaporates.
The Imposter Loop
Here's the cycle:
- You see an alert.
- You don't immediately know what it means.
- You panic internally.
- You Google it (yes, even the seniors do this).
- You find something that might be the answer.
- You second-guess yourself.
- You either escalate too early or too late.
- Repeat.
This loop is exhausting. But here's the thing — it's normal. Every single analyst who's ever sat in a SOC has gone through this. The ones who tell you otherwise are either lying or have amnesia.
What Actually Helps
Document everything. Not for compliance — for yourself. Build your own runbook. Every alert you investigate, write down what you did, what you found, and what the resolution was. In six months, that notebook becomes your superpower.
Ask dumb questions early. The cost of asking a "dumb" question in week 2 is zero. The cost of staying silent and missing a real incident in month 3 is your career.
Accept that you will miss things. Not because you're bad at your job, but because threat detection is probabilistic, not deterministic. Even the best tools have false negatives. Your job isn't to catch everything — it's to keep getting better at catching things.
The fear never fully goes away. But it evolves. It goes from "I don't know anything" to "I know what I don't know" to "I know where to look." And that progression? That's called growth.